

Updated October 26, 2026: We have updated the content. Thank you for your patience.
[What and why]
To improve transparency and troubleshooting for Microsoft Purview role-based access control (RBAC), we are enhancing audit logging for permission checks performed in the Microsoft Purview portal. These new audit records will provide administrators with clearer visibility into role and scoped-role authorization decisions, helping them investigate access issues and better understand how access evaluations are performed.
This message is associated with Microsoft 365 Roadmap ID 569363.
[Rollout schedule]
- General Availability (Worldwide): Beginning in late September 2026 and expected to complete by late October 2026
[Impact on your organization]
Who is affected
- Microsoft Purview administrators and compliance administrators who review audit logs for access investigations and troubleshooting
Platforms and services
- Microsoft Purview portal
- Microsoft Purview Audit
What will happen
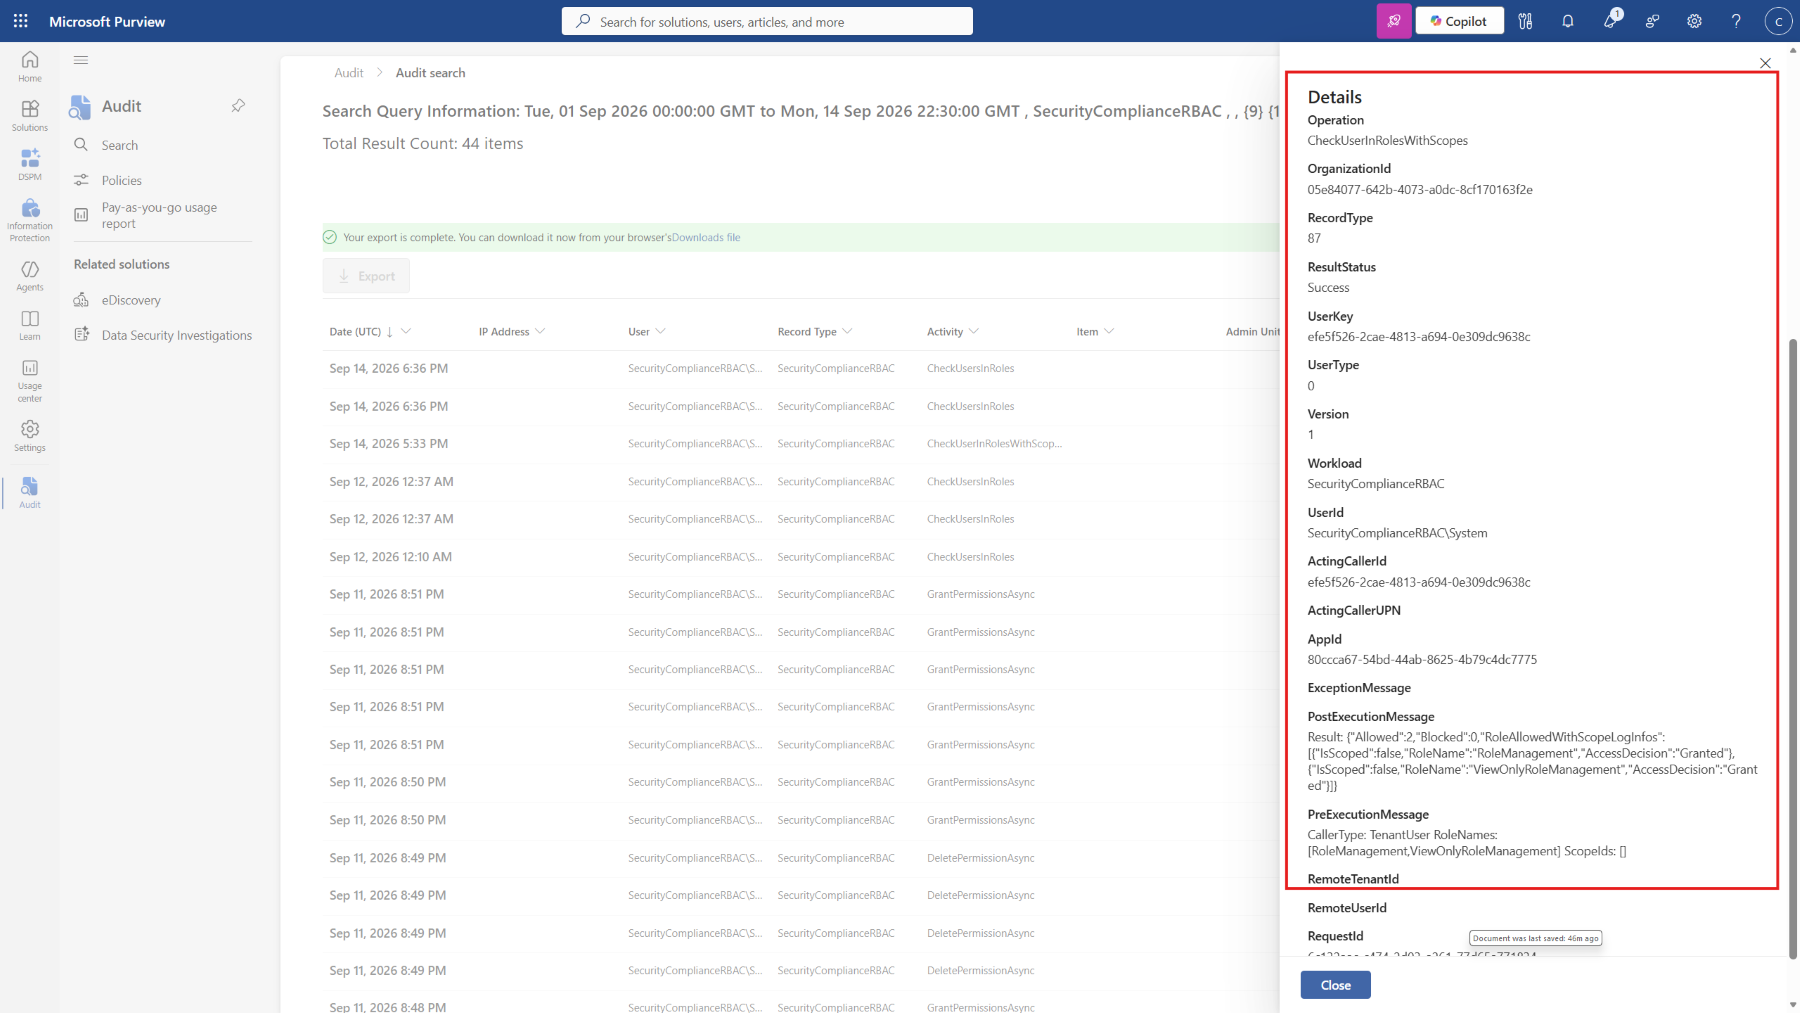
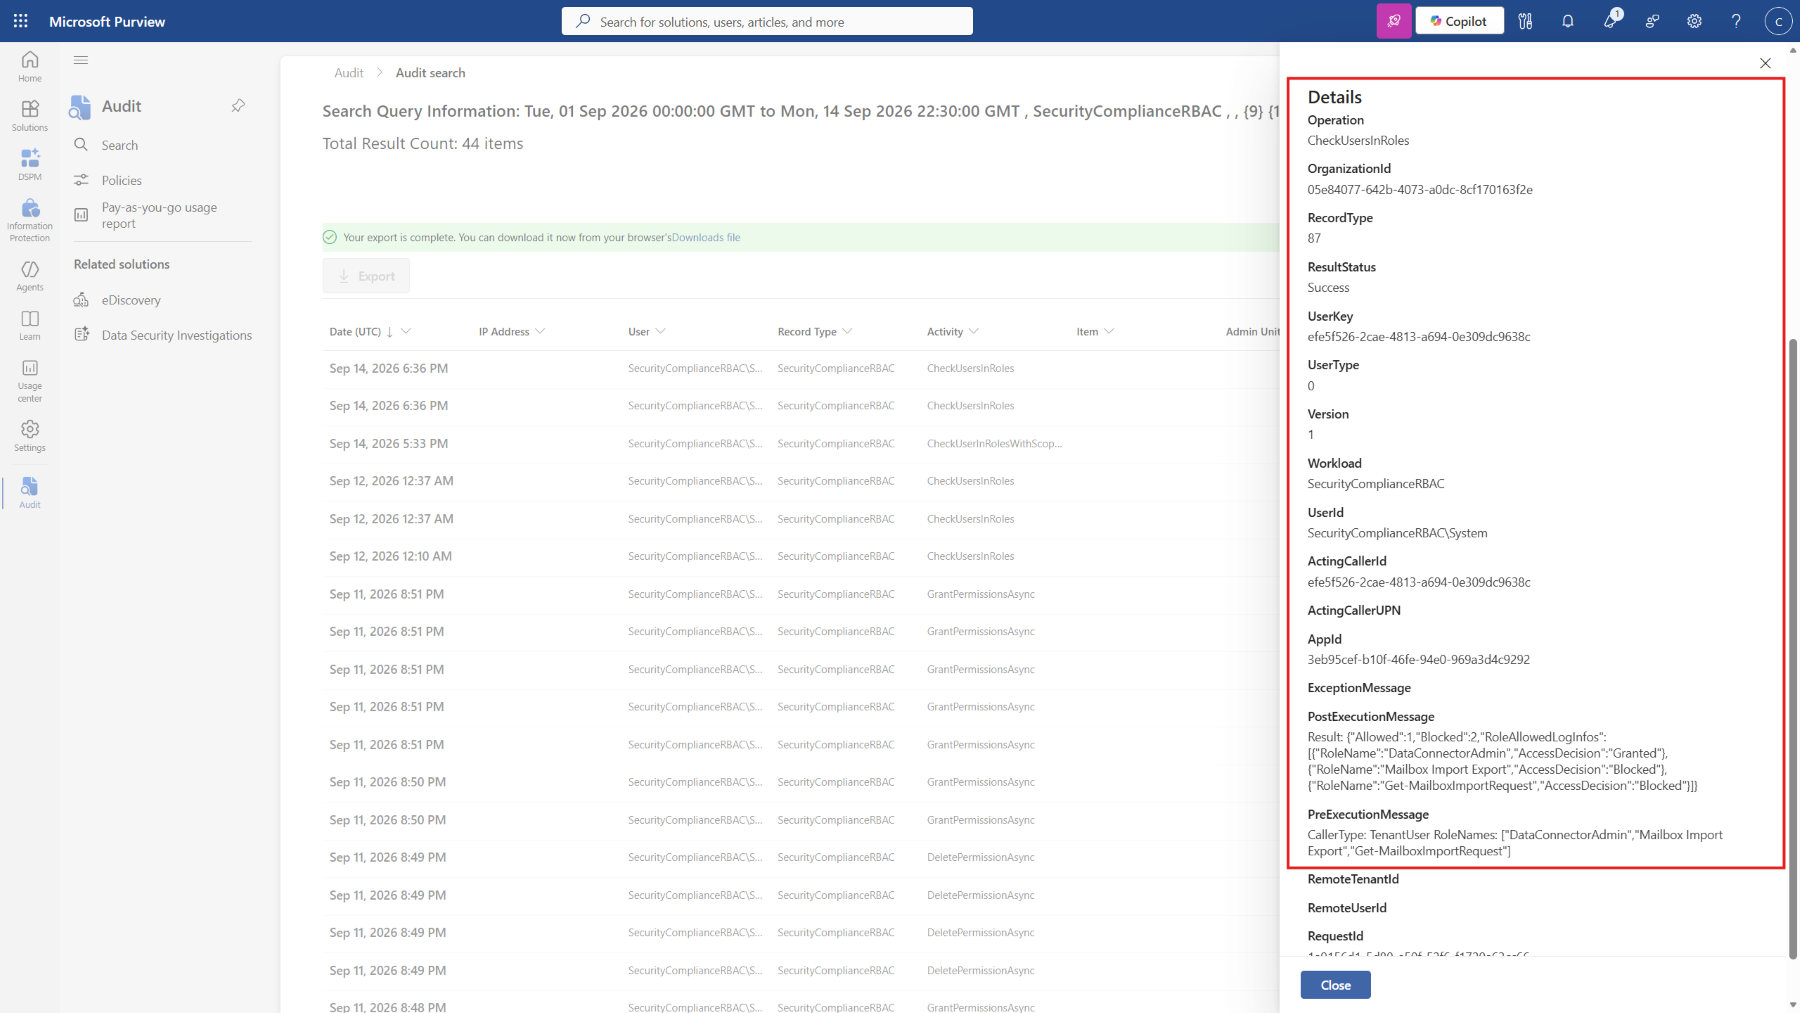
- New audit records will be generated when access checks are performed in the Microsoft Purview portal.
- Two new audit operations will be available:
- CheckUsersInRoles
- CheckUserInRolesWithScopes
- Administrators will be able to review these audit records as part of SecurityComplianceRBAC audit activities.
- The enhancement is enabled by default and requires no configuration.
- Audit records will only be generated for access checks that occur after the feature is deployed.
- No historical or retroactive audit records will be created for prior access checks.
- There is no impact for organizations.
- Supported permission-assignment and role-group change audit records will include the ClientPortal field within PreExecutionMessage, helping administrators distinguish changes initiated from Microsoft Purview and Microsoft Defender.
- Supported activities for portal attribution
- Permission assignments: Granting, updating, or removing permission assignments.
- Role groups: Creating, updating, or deleting role groups.
- Supported activities for portal attribution
- Expected ClientPortal values:
- Microsoft Purview portal: "ClientPortal": "Microsoft Purview"
- Microsoft Defender portal: "ClientPortal": "Microsoft Defender"
RBAC audit-CheckUserInRolesWithScopes:
RBAC audit-checkusersinroles:
[Action required and recommendations]
No action is required. We recommend that administrators:
- Review internal monitoring and audit procedures to determine whether the new audit activities should be included in access investigations.
- Inform compliance and security teams about the availability of the new audit operations.
- Update any internal documentation or reporting processes that reference Microsoft Purview RBAC audit data.
Learn more
[Compliance considerations]
| Question | Answer |
| Does the change modify, interrupt, or disable audit logging capabilities? | Yes. The change enhances audit logging capabilities by adding two new audit operations. |
| Does the change alter how admins can monitor, report on, or demonstrate compliance activities? | Yes. Administrators gain additional audit visibility into RBAC access evaluation outcomes, improving monitoring and troubleshooting capabilities. |